flutter_secure_storage: secrets behind platform keychains
flutter_secure_storage: secrets behind platform keychains
flutter_secure_storage is useful because it focuses on Keychain, Keystore, encrypted shared preferences, and migration. The important engineering move is to place the package behind a clear boundary, so your Flutter UI depends on a stable capability rather than a vendor-shaped API.
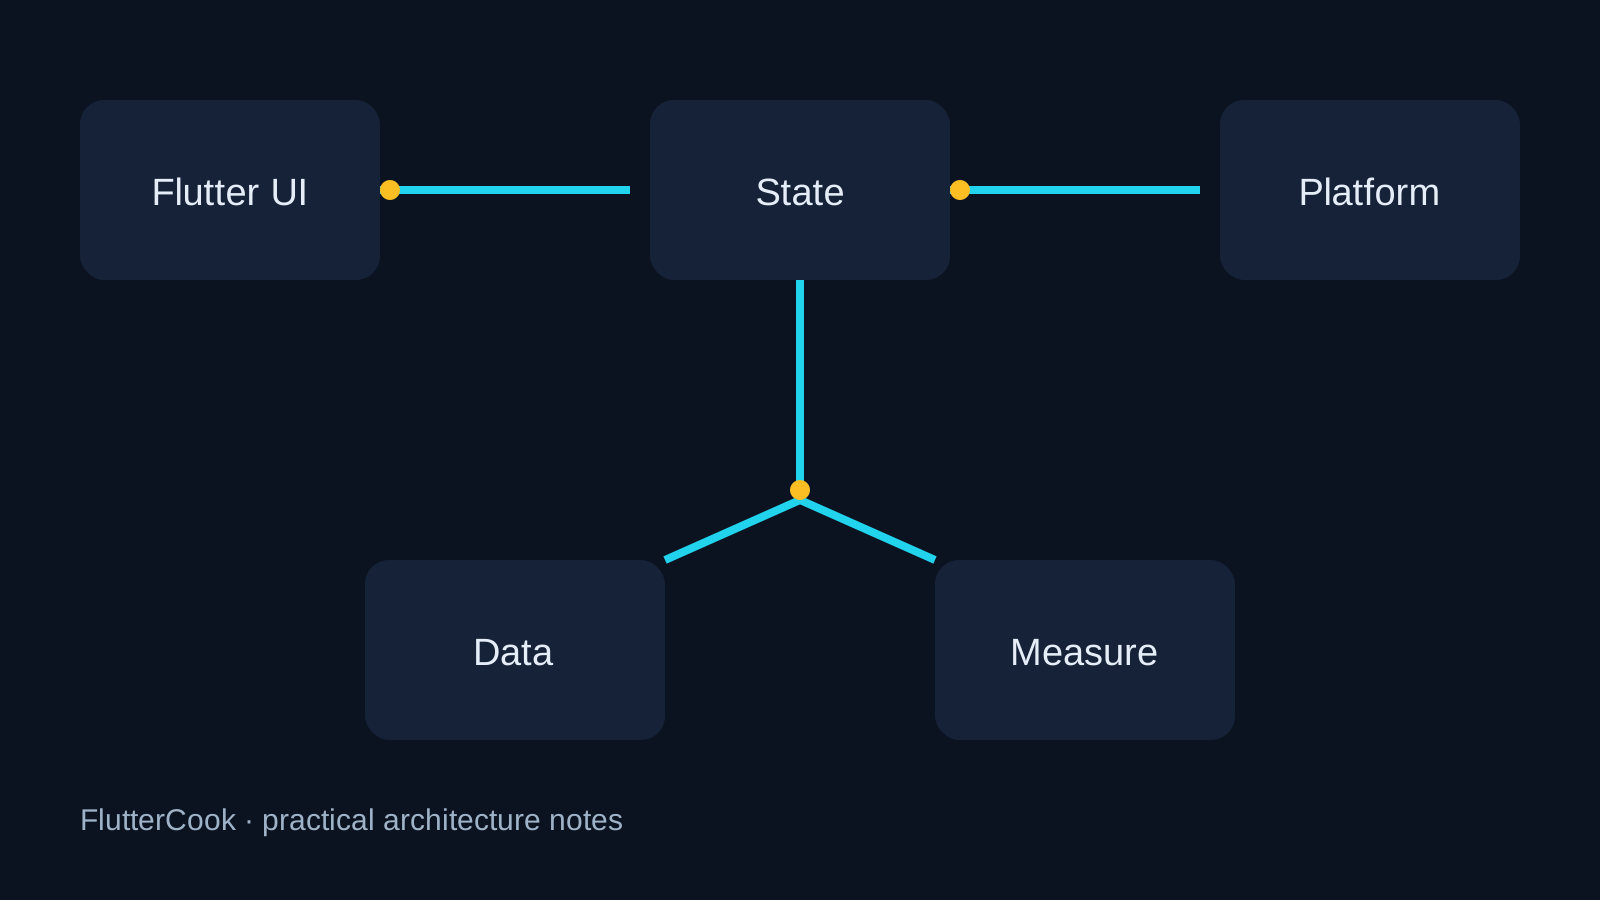
What the library should own
- Keep package calls inside a named adapter or feature boundary.
- Make lifecycle, errors, and loading state part of a testable contract.
- Expose only the capability the app needs; hide implementation details from the whole tree.
A focused starting point
const storage = FlutterSecureStorage();
await storage.write(key: 'refresh_token', value: refreshToken);
final token = await storage.read(key: 'refresh_token');
await storage.delete(key: 'refresh_token');
Production checklist
- Read the README and changelog for the exact version you pin.
- Add one test for lifecycle, failure, and app background/foreground behavior.
- Verify every platform your product supports, not only the developer machine.
- Record ownership, upgrade cadence, and rollback notes in the repository.
Common pitfall
Secure storage is for small secrets, not an offline database or a replacement for server-side revocation.
Takeaway
A good open-source library does not replace architecture. It makes one difficult boundary clearer, observable, and easier to replace.